How a Local TOTP Generator Computes Your 2FA Codes
Time-Based One-Time Passwords (TOTP) turn a shared secret and your computer's clock into short-lived verification codes. Explore the RFC 6238 algorithm parameters, hash choices (SHA-1, SHA-256, SHA-512), and why computing codes locally inside Secure TOTP Authenticator is safer than using web-form OTP generators.
This page intentionally does not host an online secret input box. Submitting a real Base32 secret key to an online web calculator risks exposing your permanent 2FA seed via network logs, analytics scripts, or third-party browser context. Use a local authenticator installed on your machine—like Secure TOTP inside Chrome—where keys remain strictly local.
Secure TOTP Authenticator is an independent browser extension developed by GreeLogix. It is not affiliated with, endorsed by, or officially connected to Google or Google Authenticator.
How Time-Based One-Time Passwords Are Calculated
Specified in RFC 6238 as a time-indexed extension of HOTP (RFC 4226), every valid TOTP code passes through four deterministic steps on your device:
Your otpauth:// URI or QR payload yields a Base32-encoded byte secret key shared once between the website and your authenticator.
Current UTC Unix time (seconds since Jan 1, 1970) is integer-divided by the step interval (30s or 60s) to form an 8-byte counter T.
Your computer hashes counter T using the shared secret key via HMAC-SHA-1 (20 bytes), HMAC-SHA-256 (32 bytes), or HMAC-SHA-512 (64 bytes).
Dynamic truncation picks a 31-bit integer offset from the HMAC digest and takes modulo 10^6 (6 digits) or 10^8 (8 digits).
Supported Algorithms, Lengths & Periods
While older apps hardcode SHA-1, 6 digits, and 30 seconds, enterprise IAM systems and developer tools sometimes specify custom parameters in their otpauth://totp/ URI. Secure TOTP generates codes across the full matrix locally:
Standard SHA-1 compatibility for consumer sites plus SHA-256 and SHA-512 support for stricter enterprise Identity Providers and developer portals.
Generates standard 6-digit passcodes alongside 8-digit tokens where higher per-step entropy is enforced.
Supports standard 30-second rotation as well as 60-second windows with accurate countdown feedback inside the Chrome popup.
Raw TOTP Generator vs. Complete Authenticator Application
Generating a single one-off code from a typed key is only 10% of real daily 2FA management. Here is why most users need a full authenticator extension rather than a stateless code calculator.
Bare Stateless TOTP Generator
- • Forces you to re-enter or store raw Base32 keys elsewhere
- • No QR code scanner or Google Authenticator export import
- • No search across dozens of accounts or issuer labels
- • No password-encrypted backup export/restore workflow
- • High risk if hosted as an online website collecting pasted keys
Secure TOTP Authenticator Extension
- Local calculation inside Chrome—zero secret transmission
- QR screenshot drag/drop, Google Authenticator bulk import & manual mode
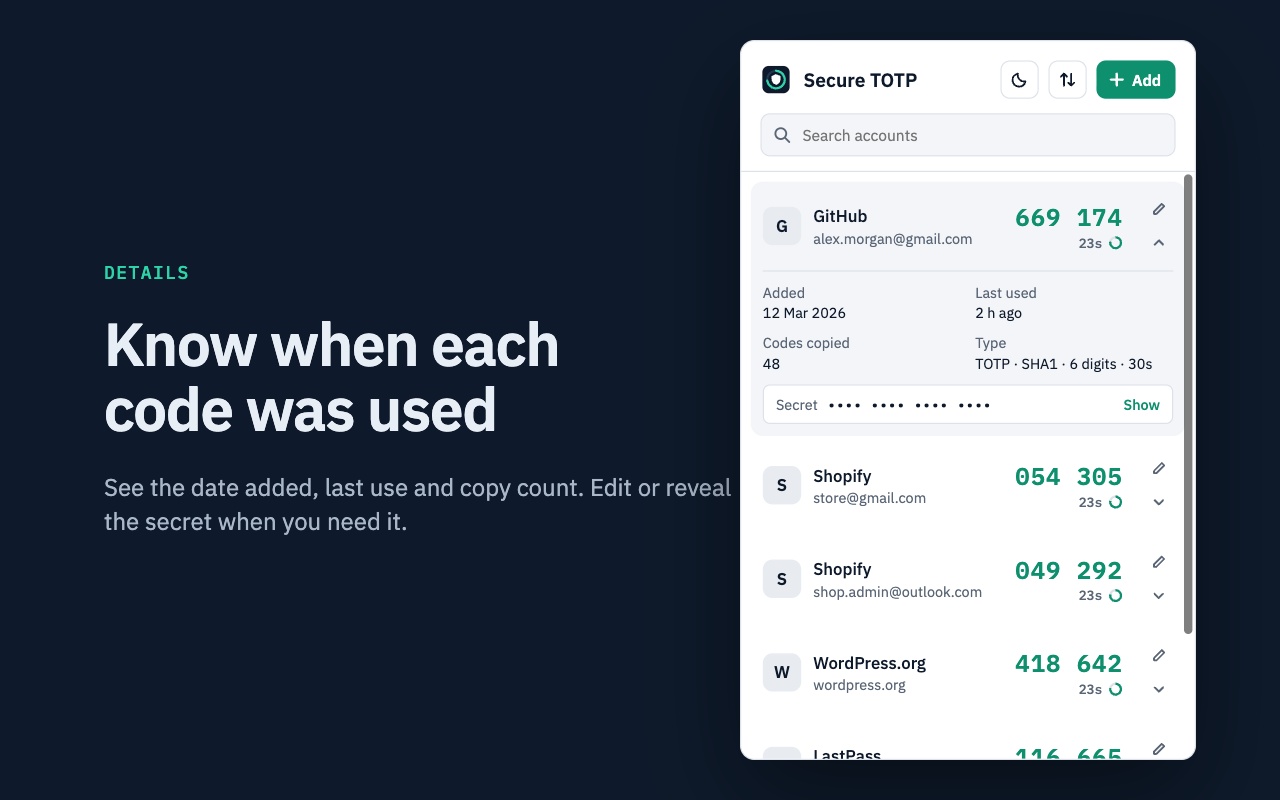
- Account search, customizable titles, copy count & Show/Hide secret toggle
- Supports SHA-1, SHA-256, SHA-512, 6/8 digits, and 30s/60s steps
- Encrypted password-protected .json backup export & duplicate-safe restore
Run Local TOTP Code Generation Directly in Chrome
Skip insecure web forms. Install Secure TOTP Authenticator to compute SHA-1, SHA-256, and SHA-512 verification codes offline on your computer.
Frequently Asked Questions
Direct answers covering compatibility, security boundaries, offline behavior, and backups.
Related Secure TOTP Guides & Resources
Explore specialized guides on desktop 2FA, offline TOTP generation, and backup security.
Extension Workflows & Compatibility
Run an RFC 6238 desktop authenticator inside Chrome on Windows, macOS, or Linux with fast search, one-click copying, and computer security best practices.
Understand how Secure TOTP computes 6- and 8-digit verification codes locally using your device clock and secret key—even completely offline.
Explore QR screenshot scanning, instant search, live 30s/60s countdowns, and objective workflow comparisons between browser and mobile authenticators.
2FA & TOTP Educational Guides
Understand what TOTP means, how shared secrets sync with Unix time windows, why codes expire, and why TOTP beats static passwords.
Compare RFC 6238 time-based codes against RFC 4226 event counters, synchronization trade-offs, and practical hardware/software use cases.
Why backups matter, how recovery codes differ from TOTP exports, encrypted vs plain-text .json files, and safe offline backup storage.
A clear foundation on authentication factors (knowledge, possession, inherence) and why app-based OTPs outperform SMS.
Keep Your 2FA Calculations Local and Offline
Install Secure TOTP Authenticator from the Chrome Web Store—zero cloud signup required.
Add to Chrome — Free